The Side-Channel Trap: Why Mathematically Unbreakable Post-Quantum Encryption Can Still Leak
Measuring microarchitectural cache latency variances in reference Kyber/ML-KEM algorithms under shared multitenant cloud environments.
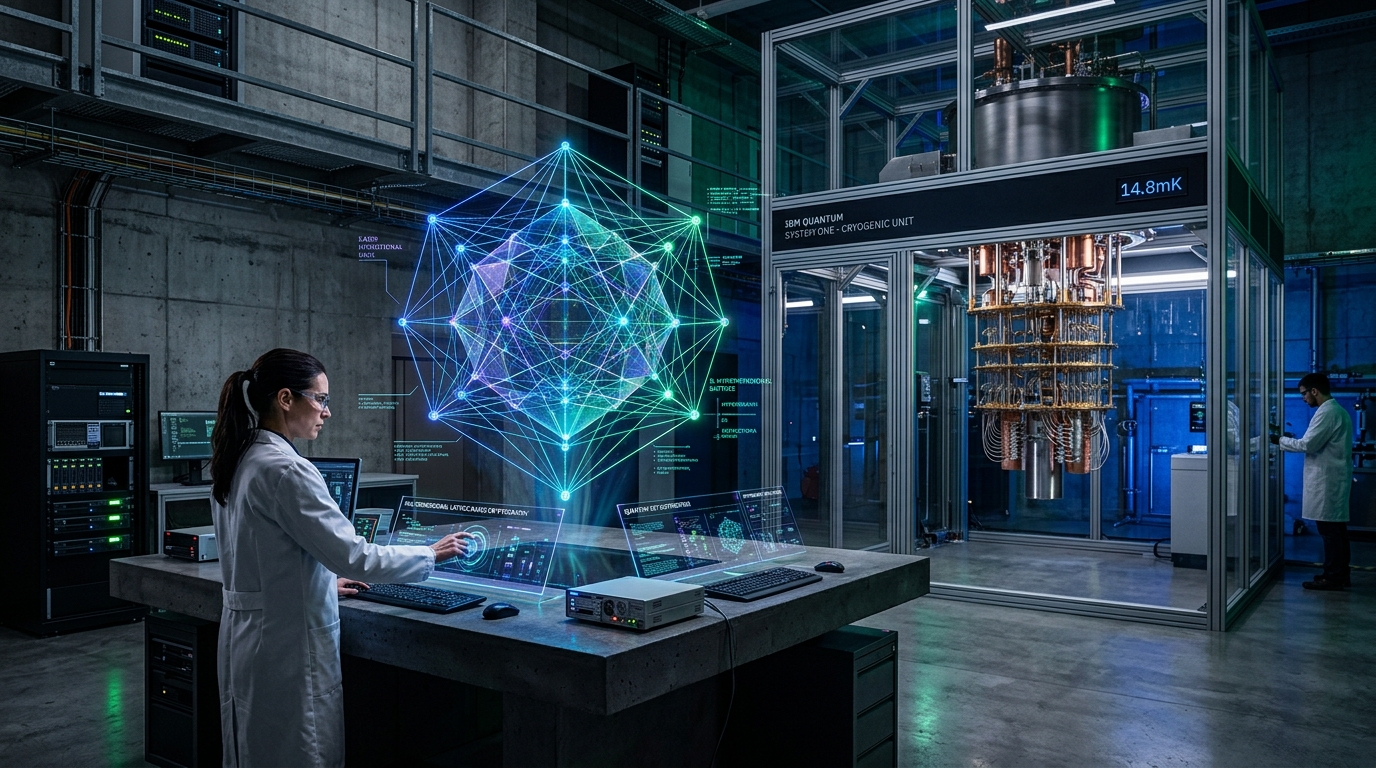
Cache Timing Vulnerabilities in Post-Quantum Lattice Implementations
As organizations begin implementing post-quantum cryptographic standards to safeguard high-assurance communications against future quantum decryption threats, the implementation security of algorithms like ML-KEM (formerly CRYSTALS-Kyber) has come under intense scrutiny.
While the underlying Module Learning with Errors (M-LWE) mathematical problem provides robust theoretical security, physical implementations running on conventional CPU microarchitectures can leak private key material through microarchitectural side-channels.
Mathematical correctness does not imply side-channel resilience. If algorithm execution time fluctuates with secret coefficients, post-quantum encryption is trivially broken.
Profiling Microarchitectural Cache Variance
In multi-tenant cloud environments where different tenants share CPU cores and L3 cache hierarchies, an attacker executing on an adjacent core can continuously probe cache lines using Prime+Probe techniques.
When ML-KEM executes polynomial multiplication over polynomial rings, memory access patterns that vary based on secret polynomial coefficients induce small, measurable latency differences. By collecting several thousand timing samples, our researchers were able to reconstruct secret key components with high confidence.
Enforcing Constant-Time Implementations
Cryptographic engineering teams must ensure that all post-quantum implementations adhere to strict constant-time paradigms:
More from The Exploit Company
Why Guardrails Fail: The Anatomy of Multi-Turn Context Bleed in Autonomous AI Agents
How incremental benign prompts across long conversation horizons gradually bleed latent state and bypass keyword safety boundaries in reasoning models.
Escaping the MicroVM: How a PCIe DMA Race Condition Collapsed Hypervisor Isolation
A deep dive into CVE-2026-44192, where an asynchronous memory race in virtual device emulation allowed unprivileged guest code to hijack the host kernel.